One workforce. One set of gates.
An agent can see what the person it works for can see - and nothing more. The fail-closed gate means if it is not allowed, it does not run. There is no separate, weaker permission system for the bots. That is the difference between "we adopted AI" and "we can let AI near real data".
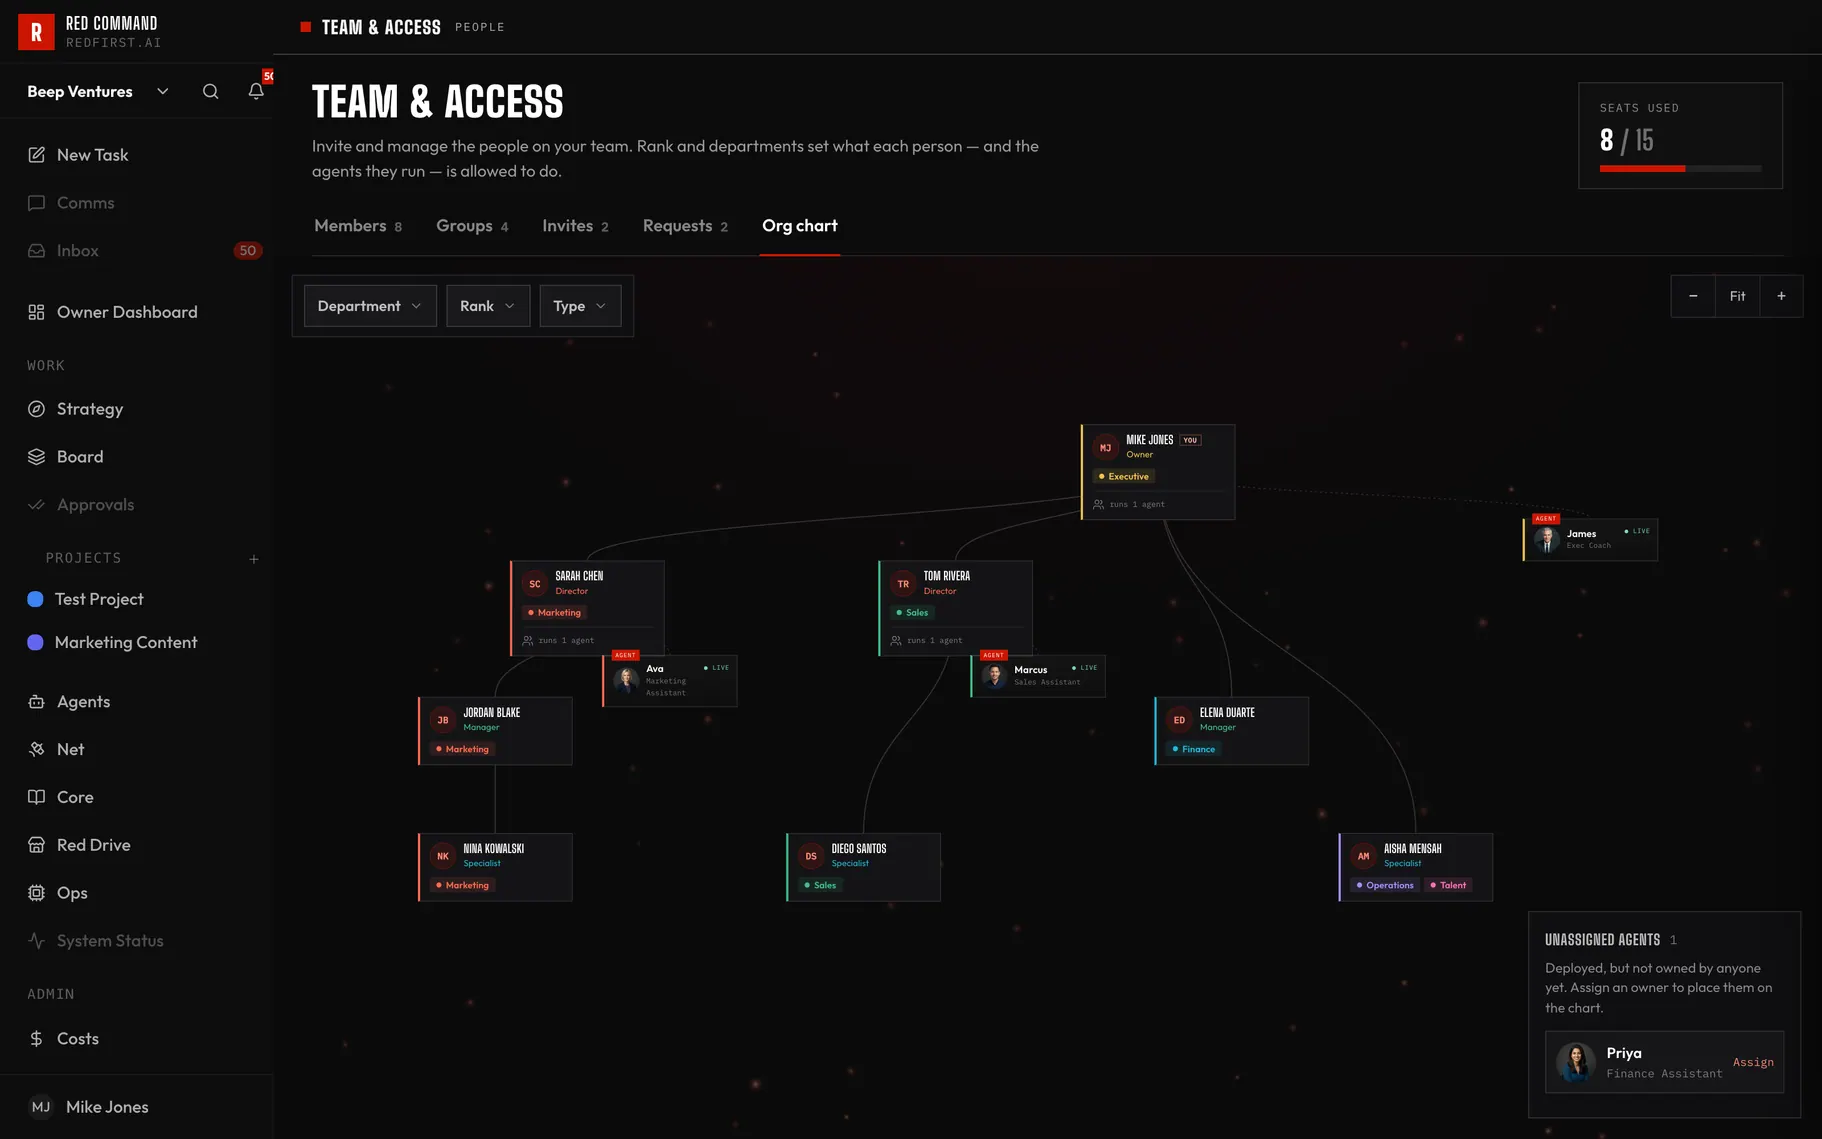
Your AI workforce, on the same chart.
A live, draggable organisation chart where agents appear alongside the humans they work for - same structure, same reporting lines, same rules.
Ranks that match a real business.
Owner, Director, Manager, Specialist, Implementer - not "admin" and "viewer". Rank and department set what each person, and the agents they run, are allowed to do.
Give a team an agent.
Groups are teams with shared agents attached - give Marketing a shared strategist in one step, and its work becomes organisational knowledge automatically.
Humans gate the dangerous things.
One queue where everything needing a human decision arrives: agent deployments, listener and workflow go-lives, budget top-ups, high-risk actions - and every client deliverable before it leaves the building.
Nobody runs up a five-figure bill.
Every agent carries a budget. When it is spent, the agent stops and files an approval request rather than quietly continuing. Spend against budget is visible in real time.
Most AI adoption stalls right here.
Not on capability - on the question nobody can answer: what exactly will it be able to see? A separate permission model for agents means a second thing to audit, and a second place for it to be wrong.
Agents are principals like people. The same rank, the same departments, the same explicit grants, the same fail-closed gate. There is no "bot permissions" screen to reconcile with the real one.
At the data layer, not in each screen that happens to remember. An agent structurally cannot retrieve what its principal is not cleared for.
"It can see what the person it works for can see." That is the whole answer, and it is the one that gets AI past a security review.
Governance is one component.
Answer the security question before it is asked.
A Red Brief maps your departments, ranks and grants onto the workforce you would actually run.
Book a Red Brief